
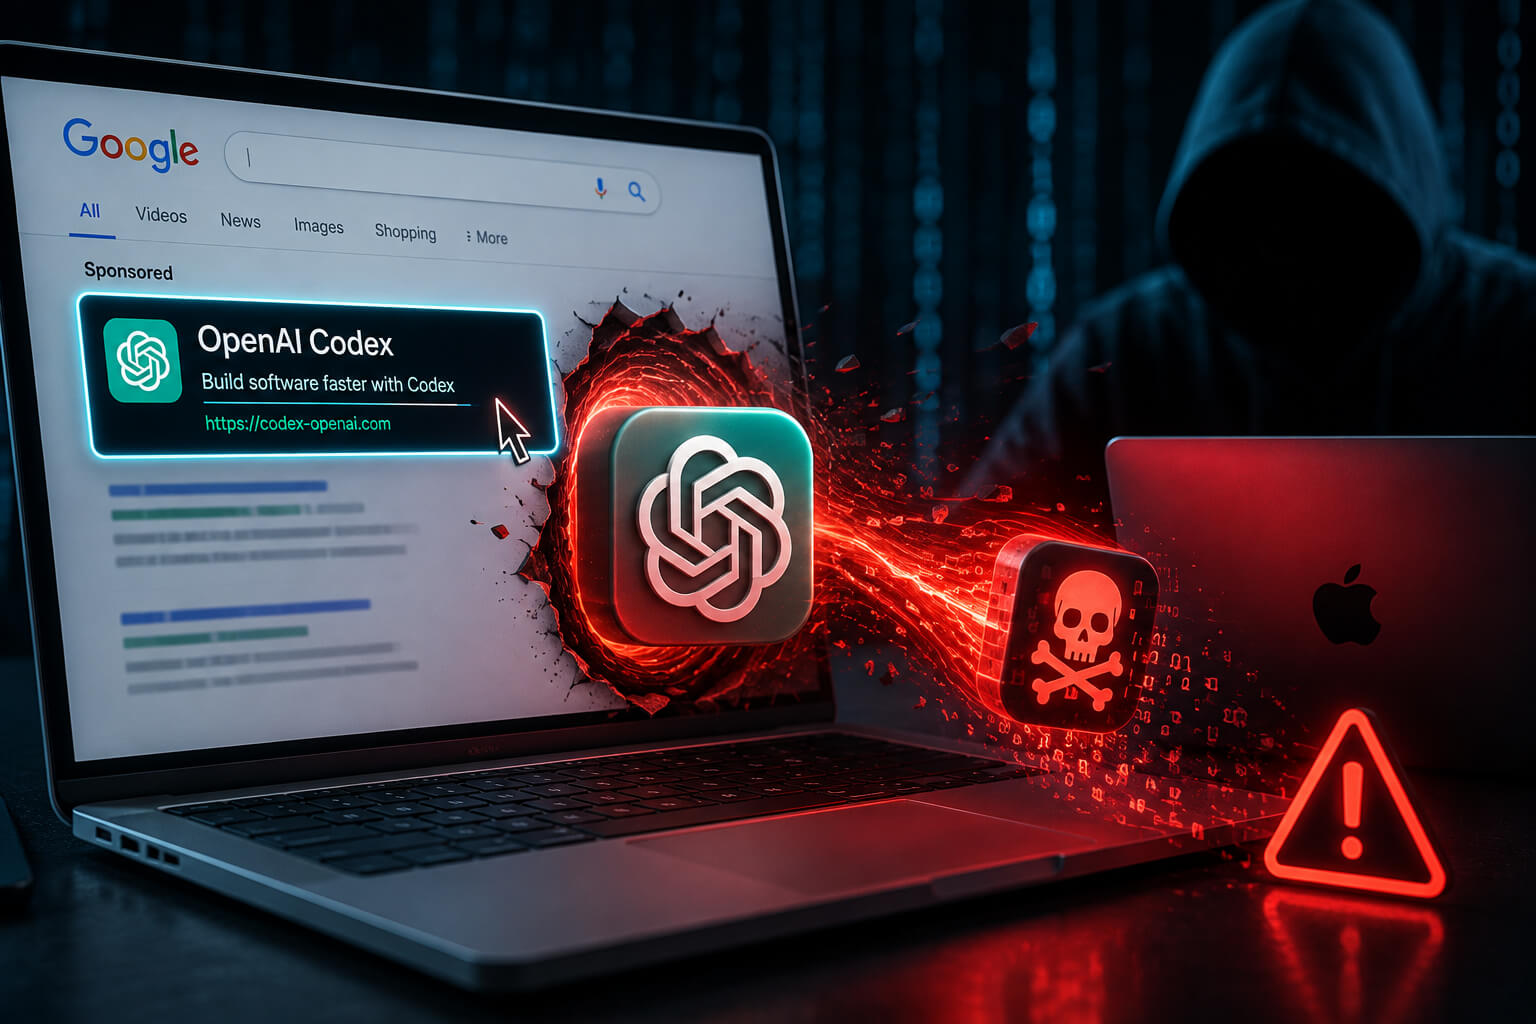
Searching Google for an AI coding tool should be routine. Recently, however, fake OpenAI Codex ads have resulted in a malware trap for some Mac users. For some Mac users, it became a malware trap.
Cybercriminals are buying sponsored search ads that pretend to offer OpenAI Codex downloads. The ads lead developers to convincing fake pages hosted through Google Sites. Those pages use OpenAI branding and look believable at first glance.
There is no real Codex installer waiting there.
Instead, users are told to open Terminal and paste a command. That command quietly starts a multi-stage malware infection. Researchers at Cato Networks say the campaign shows strong similarities to Atomic macOS Stealer, or AMOS.
Sponsored Google Results Are Being Used as the First Trap
The attack begins with something developers do every day: search Google. Cato Networks found sponsored results targeting queries such as “Codex macOS download.” Those advertisements could appear above legitimate results. Clicking them sent users to Google Sites pages made to look official. The familiar Google domain adds another layer of trust. That makes the fake page easier to overlook.
The Fake Codex Page Does Not Actually Download Codex
The landing page shows download options for macOS and Linux. Cato only observed active malware delivery to Mac users. Rather than offering a normal installer, the page tells visitors to open Terminal. It then asks them to copy and run a supplied command. The instruction is presented as a normal installation step. That is where the attack moves from impersonation into execution.
Attackers Are Using the ClickFix Technique
The campaign relies on a social-engineering method known as ClickFix. It works differently from a traditional malicious attachment. The attacker convinces the victim to run the dangerous command themselves. In this case, the command starts with text that resembles a legitimate Codex installation. Hidden behind it is code that retrieves another script. That script is then passed into the Mac’s shell.
Huntress Says the Attack Exploits Developer Muscle Memory
Dray Agha, senior manager of security operations at Huntress, said the campaign shows how macOS attack methods are becoming more focused on social engineering. Instead of relying on a simple rogue download, attackers are taking advantage of habits developers already have.
Agha said ClickFix-style attacks work because users are persuaded to run commands themselves. That helps attackers move around some traditional security controls. Developers are especially attractive targets because command-line installers are part of normal daily work.
He also warned that search ads and Google Sites make the initial lure more convincing. Trusted platforms can hide malicious infrastructure and make a fake page look legitimate. According to Agha, organizations should tighten software provisioning rules. Endpoint monitoring should also treat unverified Terminal scripts with caution, even when the source page looks official.
Agha said:
“Because developers rely heavily on command-line installers daily, attackers are betting on muscle memory over caution.”
His comments reinforce the central problem in this campaign. The attackers are not only exploiting software. They are exploiting familiar behavior.
The Malware Arrives Through Several Stages
Once the victim runs the Terminal command, the infection does not arrive all at once. Cato documented a three-stage delivery chain. The first script contains an encoded second stage. That stage reports execution and downloads the final payload. The malware is placed in a temporary directory. It is then made executable and launched. This layered approach makes the campaign harder to inspect quickly.
The Malware Tries to Reduce macOS Security Warnings
The attack also takes steps to weaken some of the warnings Mac users might normally see. The second-stage script clears extended file attributes. Those attributes can contain macOS quarantine information. Removing them can reduce the warning context presented to the user. The payload is then launched after its permissions are changed. It is a small technical step, but an important one for the attacker.
Both Intel Macs and Apple Silicon Machines Can Be Targeted
Cato found that the final payload uses a universal Mach-O format. That means it can execute on older Intel-based Macs and newer Apple Silicon systems. The attack is not limited to one Mac generation. Researchers observed components designed for both major architectures. That wider compatibility increases the number of developers the campaign can target.
Researchers See Strong Links to Atomic macOS Stealer
Cato stopped short of declaring the malware definitively to be AMOS. Still, the overlap is substantial. Researchers found similarities in how commands are decoded and how scripts are staged. They also found familiar payload locations and execution methods. The campaign uses techniques seen in earlier AMOS delivery chains. Cato described the activity as strongly consistent with that framework.
The Fake Site Changes What Some Visitors See
The criminals are also trying to make analysis more difficult. The visible Google Sites page is only part of the setup. Attacker-controlled content is loaded through an iframe. The infrastructure can examine details about the visitor. Someone using the wrong device may receive harmless content instead. Automated scanners can therefore miss the actual malware page.
OpenAI Codex Is Not the Only AI Tool Being Impersonated
The campaign extends beyond OpenAI branding. Cato also found a ClickFix landing page pretending to offer Anthropic’s Claude Code. Researchers said it reused infrastructure seen in the Codex operation. That suggests attackers are rotating recognizable AI developer brands. Popularity works in their favor. The more people search for a new AI coding tool, the larger the pool of potential victims becomes.
AI Developer Tools Have Become Valuable Phishing Bait
The lure makes sense from an attacker’s perspective. Developers are comfortable installing packages and running shell commands. AI coding products are also changing quickly. Users often search for setup instructions instead of relying on software they already know.
That creates an opening for malicious ads and lookalike download pages. The fake page does not need a sophisticated exploit. It needs trust. A sponsored Google result looks familiar. Google Sites looks familiar. Codex looks familiar. Even the Terminal command can appear legitimate at first.
Developers Should Verify AI Tool Downloads Before Running Commands
The simplest defense is also easy to ignore. Developers should verify the official source before installing AI tools. Sponsored search results deserve extra scrutiny. A page asking users to paste an unfamiliar command into Terminal should also be treated cautiously.
Organizations have another role to play. Software provisioning policies can reduce the number of unverified tools installed by employees. Endpoint monitoring can also flag suspicious shell activity. Huntress recommends treating copy-pasted Terminal commands with extreme suspicion when their origin cannot be verified.
This campaign is another reminder that AI security is not only about model attacks or prompt injection. The surrounding ecosystem is now a target too. Attackers are borrowing trusted AI brands because developers already want the software. Sometimes the malware does not need to break in. It only needs to look like the tool someone was already searching for.
Sources
- The Register — Crooks push Mac malware through fake OpenAI Codex ads
https://www.theregister.com/security/2026/08/25/crooks-push-mac-malware-through-fake-openai-codex-ads/5291899 - Cato Networks — When Trust Becomes the Payload in a Fake Codex ClickFix Campaign
https://www.catonetworks.com/blog/cato-ctrl-when-trust-becomes-payload-in-fake-codex-clickfix-campaign/ - Huntress — ClickFix-style threat analysis
https://www.huntress.com/
